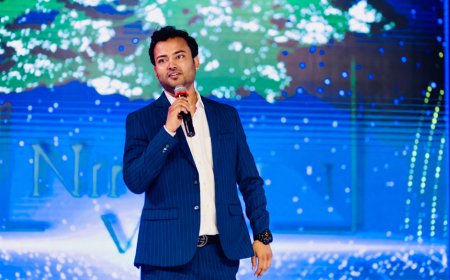
“The expectations placed on India’s SMEs are changing rapidly. As businesses digitise and become part of larger supply chains, protecting their data can no longer depend on whether they can afford a dedicated IT or cybersecurity team. Security needs to be built into the infrastructure itself, making it simpler for smaller businesses to protect critical information and maintain business continuity as they scale,” says Vishal Prakash Shah, Founder and CEO of Synersoft Technologies.
For SMEs aspiring to become reliable partners in increasingly interconnected supply chains, digital readiness is no longer simply about adopting new tools. It is about ensuring that the infrastructure supporting their business is secure, dependable and capable of meeting evolving compliance requirements.
The question, therefore, is not whether SMEs should embrace technology, but whether the infrastructure available to them is ready to support their growth securely.
Digital Transformation Is Becoming a Business Necessity
The expectations placed on SMEs have changed considerably. Price competitiveness and proximity to customers remain important, but businesses seeking to work with large enterprises and multinational clients must increasingly demonstrate consistent quality, reliable delivery, effective data management and adherence to applicable security standards.
Meeting these expectations often requires investments in enterprise resource planning (ERP) systems, cloud-based collaboration platforms, digital documentation, design software and integrated production management tools. These technologies help smaller businesses improve efficiency, coordinate with geographically dispersed teams and meet customer requirements.
Yet digitisation also changes the nature of business risk. As operations move from physical records and manual processes to interconnected digital systems, an enterprise’s ability to function increasingly depends on the availability, integrity and confidentiality of its data.
For a manufacturing SME, this could mean access to production specifications, tooling designs and inventory records. For a service provider, it might include client databases, financial information and contractual documents. Across industries, these digital assets are becoming central to business continuity and competitiveness.
When Data Becomes the Business, Protection Becomes Essential
The consequences of losing access to business data can extend far beyond a temporary IT disruption. A ransomware incident, accidental deletion or hardware failure can prevent an enterprise from processing orders, accessing customer information or maintaining production schedules.
Reconstructing years of operational records, customer histories and proprietary specifications may be expensive, time-consuming or, in some cases, impossible. For businesses operating with limited cash reserves and narrow margins, even a short interruption can affect customer confidence and revenue.
Data theft presents a different but equally serious challenge. Unauthorised access to pricing strategies, customer lists, product designs or manufacturing processes can expose an SME to competitive exploitation and reputational damage. The business may continue operating, but the information that gives it a competitive advantage may no longer remain confidential.
As a result, data protection must be understood as a business continuity measure rather than merely an IT function. Protecting digital assets is essential not only to prevent disruption but also to preserve the commercial value that SMEs build over time.
A Growing Digital Footprint, but Uneven Cybersecurity Readiness
As SMEs adopt more digital tools, their technology environments become increasingly interconnected. Employees access systems remotely, vendors exchange files, customers connect through digital platforms and business applications share information across networks.
Each connection can introduce additional risks if access controls, security policies and monitoring mechanisms are inadequate. A vulnerability in one system or an employee account can potentially affect other parts of the business, particularly where security measures are inconsistent.
The challenge is compounded by resource constraints. Many SMEs do not have dedicated IT security teams, comprehensive cybersecurity policies or a clear understanding of where sensitive information is stored and who can access it. Technology investments are often prioritised around immediate operational needs, leaving security measures to be addressed after a problem emerges.
Access to skilled professionals presents another barrier. Experienced IT and cybersecurity specialists are often concentrated in larger enterprises and technology companies that can offer greater resources, specialised roles and broader career opportunities. Smaller businesses, particularly those operating outside major technology hubs, may struggle to attract and retain comparable expertise.
This creates a structural imbalance: SMEs are increasingly expected to meet the digital expectations of enterprise customers without having access to the people, budgets or infrastructure traditionally associated with enterprise-grade security.
Why SMEs Need Simpler, More Accessible IT Infrastructure
Addressing this gap requires a shift in how cybersecurity is approached. Expecting every small business to build an internal security team, deploy multiple specialised tools and continuously manage complex configurations is unlikely to be a practical solution for the wider SME ecosystem.
Instead, security needs to become more accessible, integrated and manageable. Infrastructure should be designed to minimise unnecessary exposure, restrict access to sensitive information and reduce the dependence on constant manual intervention.
One approach gaining relevance is the Zero Trust security model. Its underlying principle is that access should not be granted automatically simply because a user or device is connected to a business network. Access must be appropriately verified, restricted according to requirements and reviewed as necessary.
For SMEs, the value of this approach lies in making security a foundational part of the technology environment rather than an additional layer that must be assembled and managed independently.
The concept of ready-made, integrated IT infrastructure, sometimes described as “IT in a Box”, seeks to simplify this process by bringing essential technology and security capabilities into a more manageable setup. When appropriately designed and configured, such infrastructure can help businesses establish consistent controls without the complexity of building an enterprise-scale IT environment from scratch.
However, the effectiveness of any solution depends on its actual capabilities, implementation, maintenance and the organisation’s operating practices. No single product can eliminate every cybersecurity risk, making secure configuration, employee awareness, recovery planning and regular updates important parts of the overall approach.
Building a Stronger Foundation for Sustainable SME Growth
For India’s SMEs, cybersecurity is increasingly linked to business resilience, customer trust and long-term growth. As these enterprises become more deeply embedded in national and international supply chains, their ability to protect business-critical information will influence how confidently they can participate in a digital economy.
The focus must move beyond reacting to incidents towards building systems that reduce risk from the outset. This means making secure access, data protection, reliable recovery mechanisms and manageable IT operations part of everyday business infrastructure.
For many smaller enterprises, the objective is not to replicate the technology departments of large corporations. It is to access the level of protection necessary to operate reliably, meet customer expectations and grow without exposing the business to avoidable risks.
Is the Infrastructure Ready?
India’s SME expansion presents a significant opportunity for economic growth, innovation and deeper integration into global supply chains. Realising that opportunity, however, requires businesses to be equipped not only to adopt technology but also to manage the risks that accompany it.
The next phase of SME digitisation must therefore place secure infrastructure alongside productivity, affordability and operational efficiency. Accessible security models, simplified IT management and stronger data protection practices can help bridge the gap between what SMEs are expected to deliver and what they can realistically implement.
Ultimately, sustainable growth will depend on more than the ability to win new contracts or increase production. It will also depend on whether businesses can protect the information, systems and relationships that keep them running. For India’s SMEs, building that resilience is no longer a future consideration. It is becoming a fundamental requirement for growth.